🧠 If an AI system exposed your customer database tomorrow, would knowing whether it was conscious change the damage?
The consciousness question deserves serious investigation. It could change how society understands intelligence, moral responsibility and the treatment of future machines. But businesses have another question to answer today: what have we allowed these systems to access and do?
My argument is simple. We should remain open to evidence about machine consciousness while being much less relaxed about machine permissions.
The debate is real and the verdict is not settled
Recent expert commentary reveals disagreement about both the answer and how to investigate it.
On 8 October, philosopher Joshua P. Hochschild argued that the debate needs clearer distinctions between human-like behavior, cognition and the nature of the system producing them. His philosophical argument challenges the assumption that matching human behavior settles the question of consciousness. It does not constitute an experimental test. Read his argument. [Read his argument]
Computational linguist Emily M. Bender took a skeptical position in a 9 October Mastodon discussion, rejecting claims that language models can suffer and calling for stronger evidence. Her position is an important challenge to interpretations of fluent output as inner experience, rather than a statement of universal scientific agreement. Read the original discussion. [Read the original discussion]
There is a challenge in the other direction, too. In commentary dated 7 October, philosopher Henry Shevlin examined how usefulness, attachment and self-interest can influence whether people recognize consciousness in another entity. That warns against convenient dismissal as well as wishful projection. It is an ethical argument, not proof that current models feel anything. Read Shevlin’s analysis. [Read Shevlin’s analysis]
Earlier scientific work helps explain why confident headlines can mislead. A September preprint co-authored by Anil Seth, Murray Shanahan, Shane Legg and others proposes combining theories and indicators when assessing AI consciousness. Its illustrative conclusions vary sharply with the assumptions used. Those outputs are not measurements establishing an AI’s probability of being conscious. Read the September preprint. [Read the September preprint]
The reasonable business response is intellectual humility. Neither an impressive conversation nor a dismissive slogan should settle a question this difficult.
Preparedness without prophecy
In its 9 October report, Axios described AI crisis planning; OpenAI said the scenarios were not inevitable. [9 October report]
Preparedness is worth discussing without treating it as a prophecy. A fire drill is useful because people need to know what to do if something goes wrong. Its existence cannot tell us when a fire will happen.
For a business owner, the practical question is whether your own response has been rehearsed. Who can pause an automated workflow? Who can revoke access? Who decides whether a suspicious action is harmless, mistaken or malicious?
Those questions remain relevant whatever researchers eventually conclude about consciousness.
Evidence of misuse deserves more attention than speculation about motives
An investigation published by CrowdStrike on 7 October described AI-assisted activity targeting South Korean financial organizations. Researchers examined exposed attacker files and session histories. The number of affected organizations remained unconfirmed. The case concerns human-directed misuse of AI tools; it does not establish machine consciousness or spontaneous rebellion. Read the technical investigation. [Read the technical investigation]
That distinction matters. Assigning an imagined motive to software can distract from the people, vulnerabilities and access decisions involved.
There is also evidence of defensive effort. In an 8 October announcement, Anthropic described new support for critical-infrastructure and open-source security. It acknowledged a stubborn problem: discovering vulnerabilities is getting easier, while checking, prioritizing and fixing them remains difficult. An announced program is not proof of effectiveness, but it makes the discussion more useful than a choice between panic and complacency. Read the announcement. [Read the announcement]
The security decision your company can make now
OWASP identifies excessive functionality, permissions and autonomy as sources of risk in AI applications. Its guidance includes restricting tools and access, requiring approval for consequential actions, and enforcing authorization outside the language model. See OWASP’s excessive-agency guidance. [See OWASP’s excessive-agency guidance]
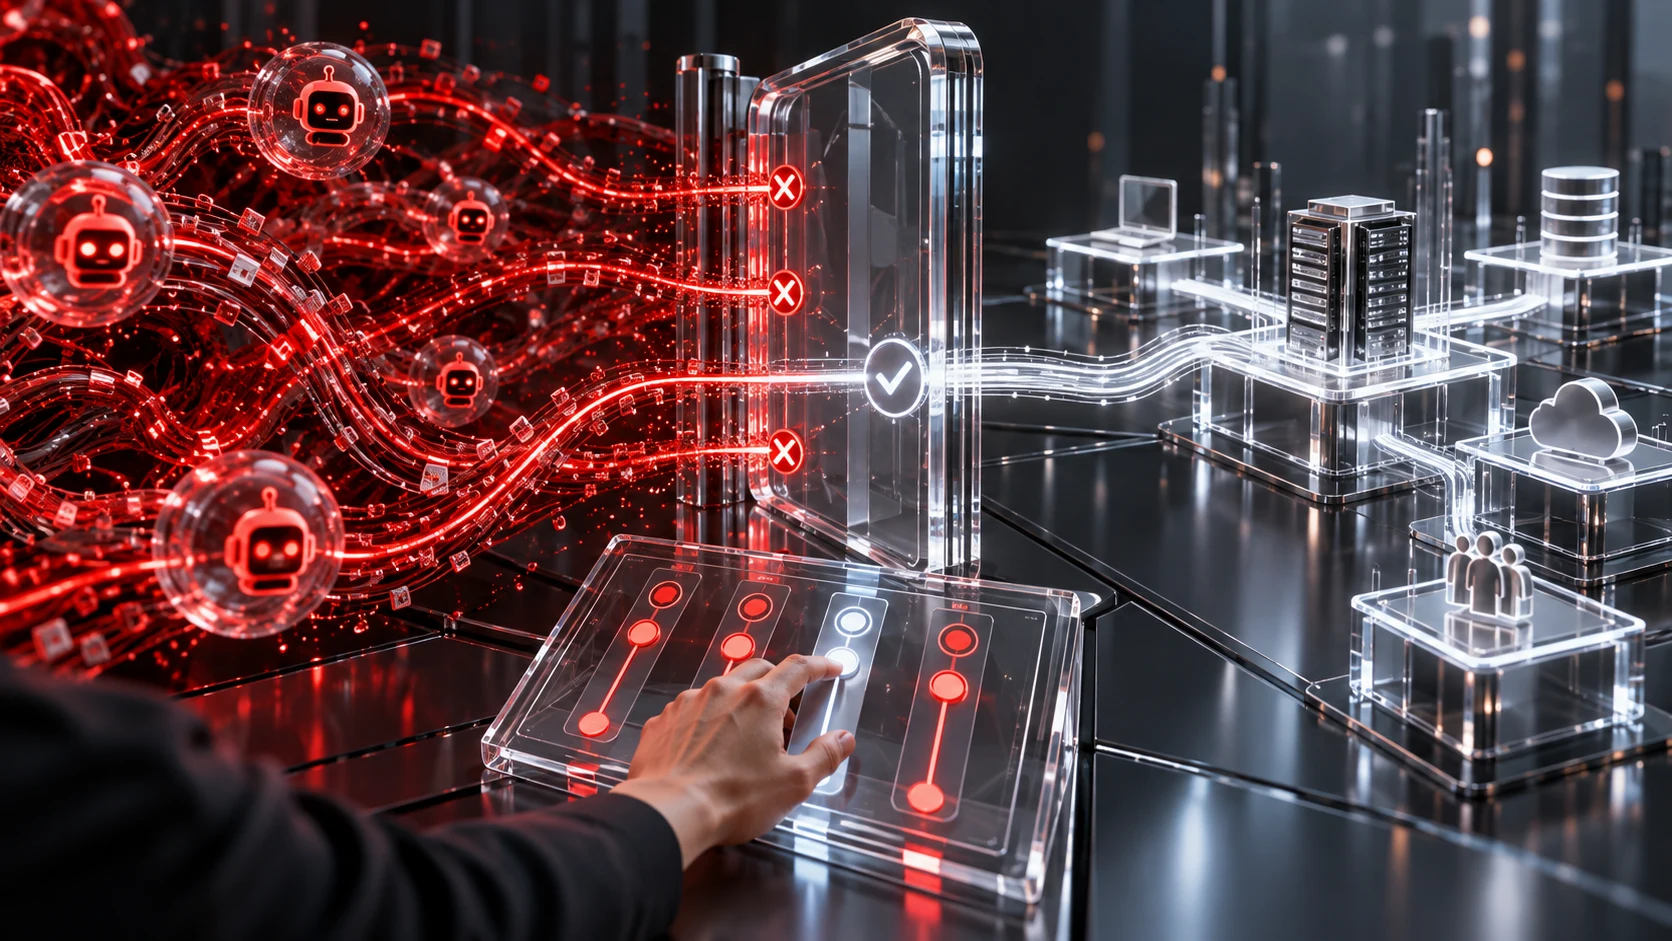
For leaders, that translates into a practical review:
- List the systems your AI can reach and the actions it can take.
- Remove permissions that are unnecessary for the job.
- Keep consequential actions behind meaningful approval.
- Establish who reviews security findings and who owns each fix.
- Test whether access can be stopped and whether the fix actually works.
A reassuring answer from a chatbot is not a substitute for checking those controls. Ask for evidence: the permission setting, the approval record, the verified result.
The goal should be to use AI confidently within boundaries you understand. That requires neither declaring machines conscious nor proving they never could be.
Turn concern into a security decision
Shofield AI’s Cyber Security AI Manager is designed to help teams review security findings, prioritize risks and prepare remediation proposals for human approval. Capabilities depend on your workspace, authorized integrations and verified setup.
Discuss your environment with us and see which capabilities fit your security workflow. Start with a clear view of what needs attention and what must be verified before action.
Discuss Cyber Security AI Manager with Shofield AI. [Discuss Cyber Security AI Manager with Shofield AI]
The consciousness debate will continue. Your responsibility for what AI can access and do is already here.